A warning has been issued by European security researchers about critical vulnerabilities discovered in PGP/GPG and S/MIME email encryption software that could reveal the plaintext of encrypted emails, including encrypted messages sent in the past.
The alert was put out late on Sunday night by professor of computer security Sebastian Schinzel. A joint research paper, due to be published tomorrow at 07:00 a.m. UTC (3:00 a.m. Eastern Time, 12:00 am Pacific) promises to offer a thorough explanation of the vulnerabilities, for which there are currently no reliable fixes.
There are currently no reliable fixes for the vulnerability. If you use PGP/GPG or S/MIME for very sensitive communication, you should disable it in your email client for now. Also read @EFF’s blog post on this issue: https://t.co/zJh2YHhE5q #efail 2/4 — Sebastian Schinzel (@seecurity) May 14, 2018
Details remain vague about the so-called "Efail" exploit, but it appears to involve an attack vector on the encryption implementation in the client software as it processes HTML, rather than a vulnerability in the encryption method itself. A blog post published late Sunday night by the Electronic Frontier Foundation said:
"EFF has been in communication with the research team, and can confirm that these vulnerabilities pose an immediate risk to those using these tools for email communication, including the potential exposure of the contents of past messages."
In the meantime, users of PGP/GPG and S/MIME are being advised to immediately disable and/or uninstall tools that automatically decrypt PGP-encrypted email, and seek alternative end-to-end encrypted channels such as Signal to send and receive sensitive content.
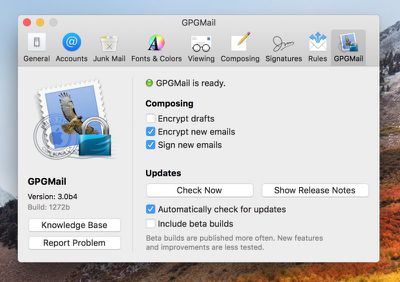
Update: The GPGTools/GPGMail team has posted a temporary workaround against the vulnerability, while MacRumors has compiled a separate guide to removing the popular open source plugin for Apple Mail until a fix for the vulnerability is released. Other popular affected clients include Mozilla Thunderbird with Enigmail and Microsoft Outlook with GPG4win. Click the links for EFF's uninstall steps.