25–35 min
Updated
 By Malcolm McDonald Founder, Editor-in-ChiefAuthor of Grokking Web Application Security
If you are vulnerable to SQL Injection, attackers can run arbitrary commands against your database.
SQL injection is an injection attack in which an attacker submits crafted input that an application pastes into a database query, changing what the query does. It happens when SQL statements are built by concatenating strings with untrusted input. Attackers use it to bypass logins, read or alter data, and delete entire tables.
- How string concatenation lets attacker input rewrite a SQL query
- How to spot an injection vulnerability from an error message and the code
- Why parameterized statements are the most reliable defense
OWASP Top 10
PCI DSS v4.0.1
-
SQL Injection lab
Attack a login form backed by a real database running in your browser. Start with a single quote that crashes the app, read the SQL error in the logs, see the vulnerable code, then use ' or 1=1-- as the password to log in.
-
How to prevent SQL Injection
The prevention guide covers four approaches, including:
- Parameterized Statements
- Object Relational Mapping
- Escaping Inputs
-
SQL Injection quiz
Three questions. Passing marks the lesson complete.
- SQL injection PortSwigger
- Exploiting SQL Injection Acunetix
- SQL Injection Cheatsheet Netsparker
- Bobby Tables xkcd
Command Execution
If your application calls out to the OS, you need to be sure command strings are securely constructed.
Regex Injection
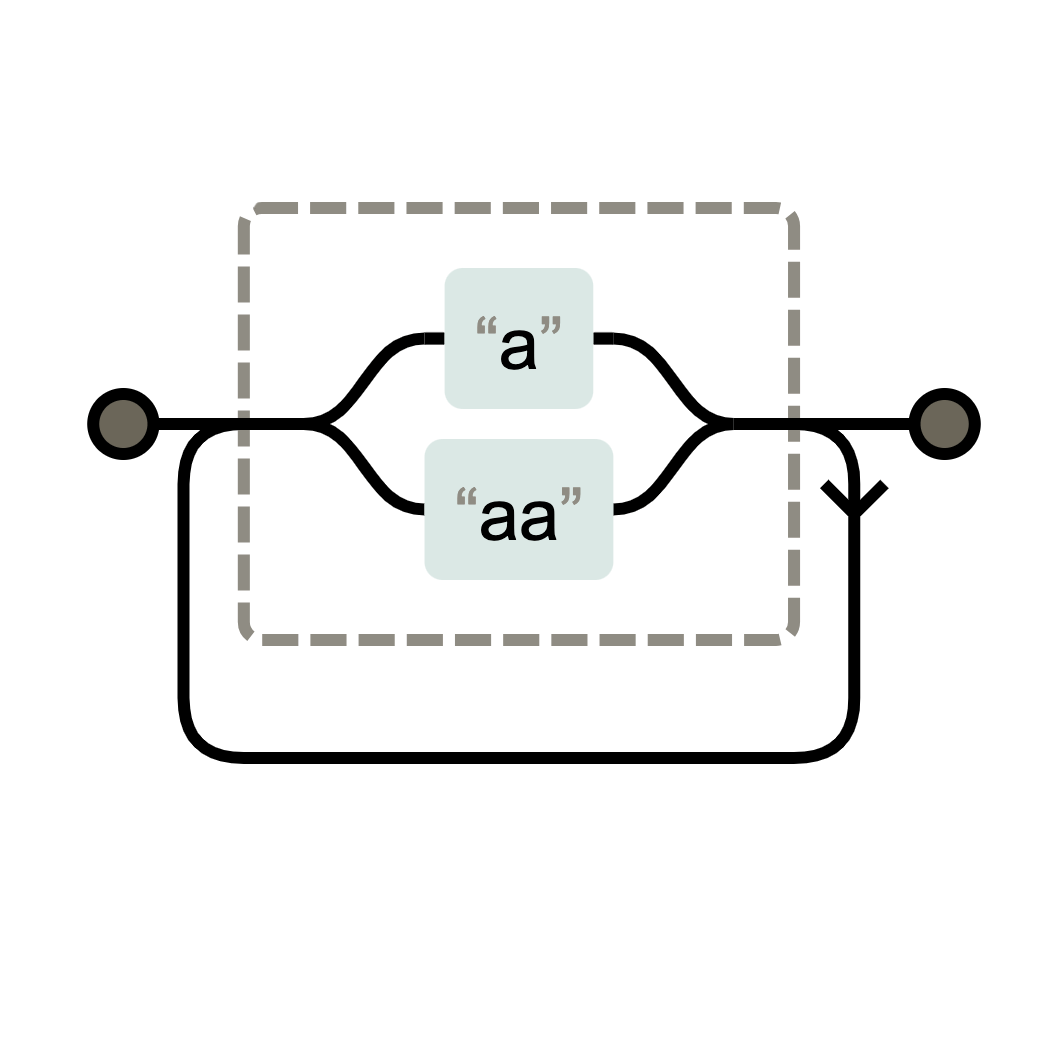
Regular expressions are frequently used in web-development, but can be abused by attackers.
Cross-Site Scripting
If your site allows users to add content, you need to be sure that attackers cannot inject malicious JavaScript.
Information Leakage
Revealing system information helps an attacker learn about your tech stack.
© 2026 Hacksplaining. Built with in Seattle, WA, USA
About Us Need help? Reach out to support@hacksplaining.com