Supply chain security alerts
Know within minutes when a compromised package, an exploited CVE, a vendor breach or an end-of-life date hits your stack
- ScanPharon lists every package, image and cloud service your repos use, on your machine.
- MatchNew compromised packages, exploited CVEs, breaches and end-of-life dates are checked against that list.
- AlertThe team that owns the repo hears within minutes, in Slack, email and Claude Code, with the secrets to rotate.
Requires Claude Code · Code stays on your machine · From $12/month · 7 days free, no card
Incidents from the sources that publish them
- OSV.dev
- GitHub Advisory
- OpenSSF
- CISA KEV
- endoflife.date
- PyPI
- Go vulndb
- RustSec
- Vendor bulletins
- Security news
OSV.dev and security news every 5 minutes. CISA KEV and end-of-life dates every day.
The alert
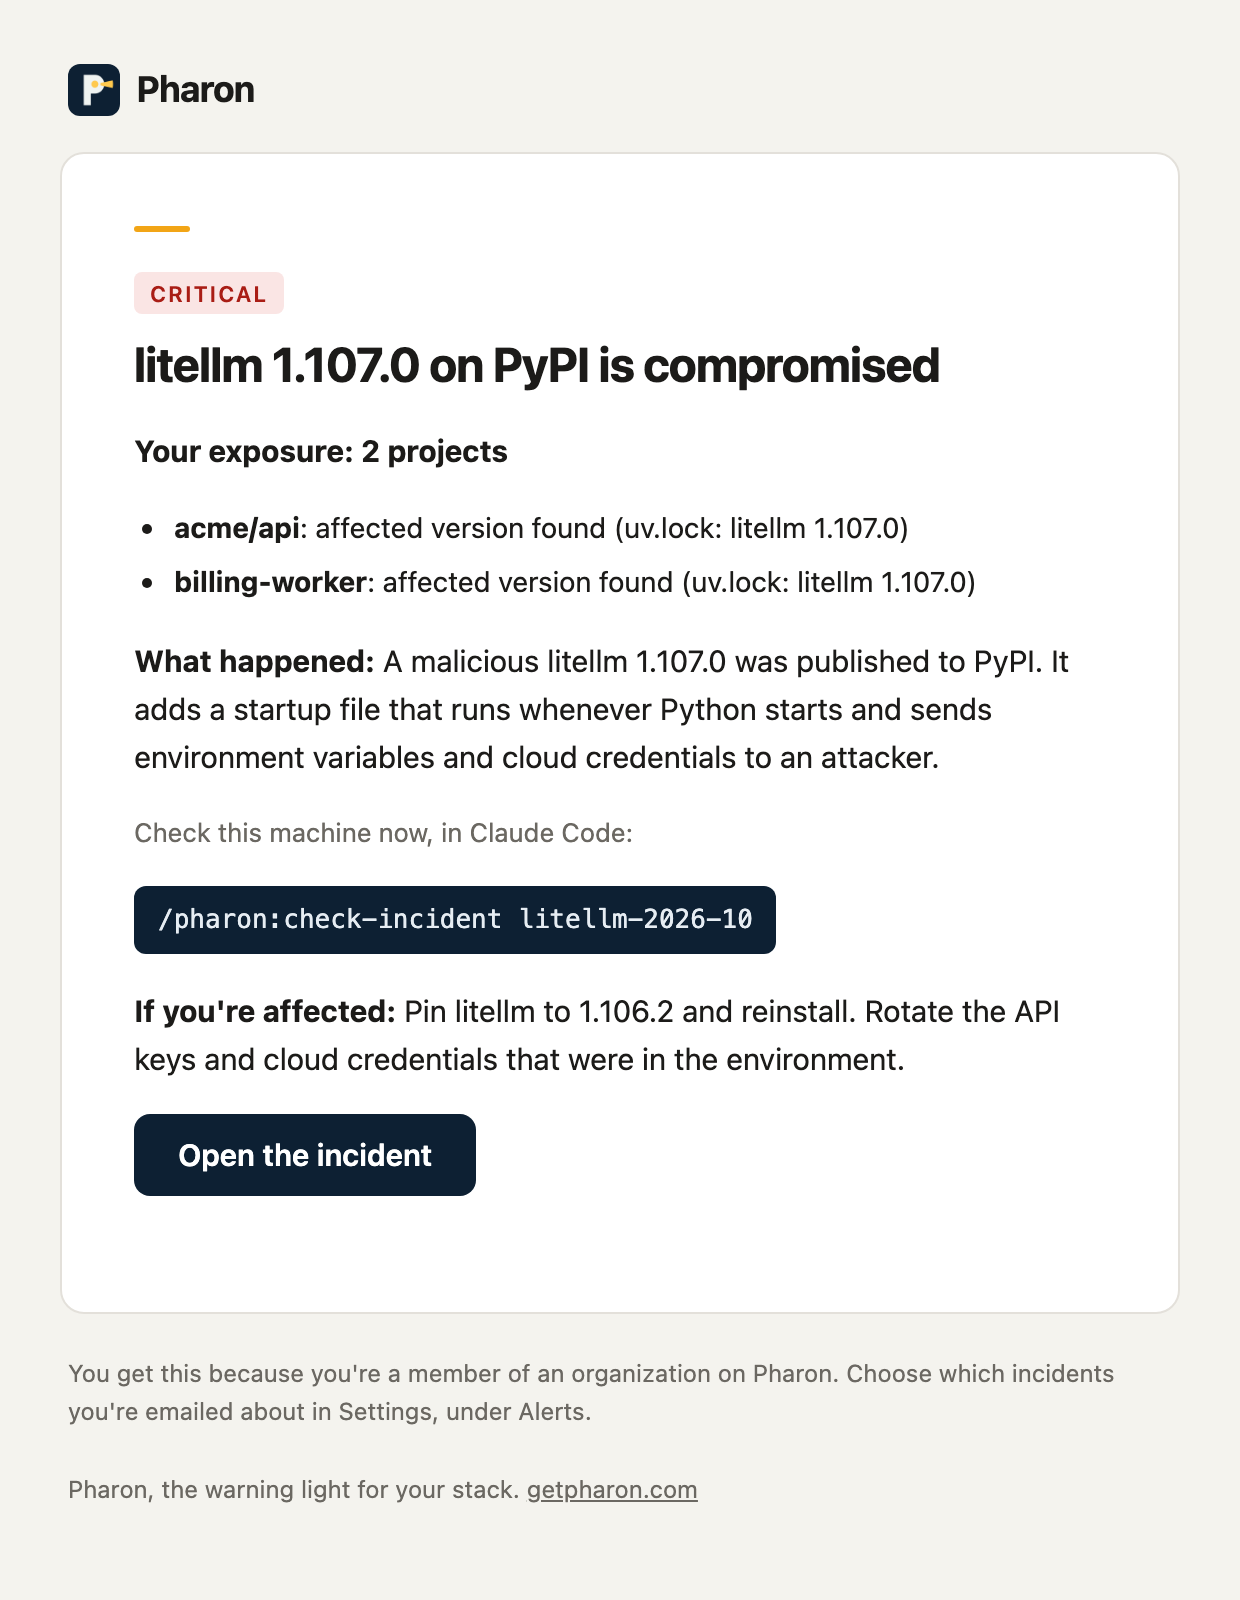
This is what lands in the owner's inbox.
Which repos are hit and where, what happened, the command that checks a laptop, and what to do if you're affected. Critical and high incidents arrive within minutes, the rest in a daily digest, and the same alert reaches Slack and your webhooks.
An example: acme is a made-up company.
- 1:14 PM
OSV.dev reports litellm 1.107.0 as compromised. Pharon publishes the signed notice litellm-2026-10.
- 1:20 PM
Matched in acme/api and billing-worker. Both pin litellm 1.107.0 in uv.lock.
- 1:20 PM
The api team hears first. Slack #security, an email, and a signed webhook.
- 1:20 PM
The light comes on in Claude Code.
🔦 critical · 1 openin the status line of both repos. - 1:26 PM
Lena runs /pharon:check-incident. Her laptop is affected through .venv and the pip cache. Rotate OPENAI_API_KEY.
- 1:31 PM
Pinned to 1.106.2 and rotated. The next inventory upload clears the match, and the light goes off.
In Claude Code
The light comes on where you work.
The plugin puts a warning light in your Claude Code status line, and a notice pops up the moment a critical incident hits the repo you're in. One command then checks this machine, read-only, and names the secrets to rotate.
Features
Built for the way you already work
Pharon meets you in Claude Code, your inbox, Slack and your pull requests.
Session notices
Open Claude Code in an affected repo and Pharon speaks first, with the command to check.
Local check
Reads lockfiles, installed packages, caches and images on this machine, without changing anything.
Rotation checklist
Secret names from shared checks become a checklist with owners. Never their values.
Branch previews
Branches and uncommitted changes are checked without replacing the official inventory.
Pull request check
The GitHub Action fails a pull request that brings in a component with an open incident.
Slack and webhooks
Critical and high incidents go out at once. Webhook payloads are signed.
End-of-life dates
Runtimes and managed databases nearing end of support show up before the deadline.
Daily digest
Everything else arrives once a day, or not at all. Snooze any incident for a week.
Let something else keep watch tonight.
From $12 a month for 10 projects, after a free 7-day trial. No card needed to start.
Start the free 7-day trialSecurity incident alerts for everything you run. Scanned on your machine, matched against new incidents all day.
/plugin marketplace add getpharon/pharon
Watching OSV.dev, CISA KEV, endoflife.date and security news
Pharon is part of Gitmore (opens in a new tab), automated reporting and insights for engineering teams.
Pharon, named after the Pharos, the lighthouse of Alexandria© 2026 GITMORE LTD, company number 16606931, England and Wales