Use AI Agents Safely and Securely
Autonomous enables organizations to use AI across endpoints with continuous shadow AI discovery, risk assessment and remediation, and real-time guardrails, all in one place.

Traditional endpoint security can't see AI agent behavior. We secure over 50 of the most popular AI agents.
Autonomous automatically maps all AI assets and uncovers hidden risks, allowing security teams to instantly find threats, remediate vulnerabilities, and secure data access.

You cannot secure or govern what you cannot see. Employees are spinning up unvetted agentic capabilities like MCPs and skills, creating massive blind spots across the enterprise.
Agents can execute unauthorized, harmful, or irreversible actions entirely on their own—even without malicious intent or explicit employee approval.
A single compromised MCP server, skill, or plugin instantly becomes a backdoor straight into your network.
Without inline controls, a single prompt injection or off-script agent behavior can instantly escalate into a full enterprise breach.
Agents continuously utilize sensitive corporate data and source code across environments potentially leaking data.
Agents accumulate unmanaged credentials and permissions, carving out direct access paths to core enterprise systems while dramatically increasing your attack surface.
Autonomous restores control over agent execution, with a focus on the endpoint, through a pluggable security engine built to evolve with the AI ecosystem. Connect it wherever AI runs, enforce security consistently, and integrate the outcomes into your existing security stack.
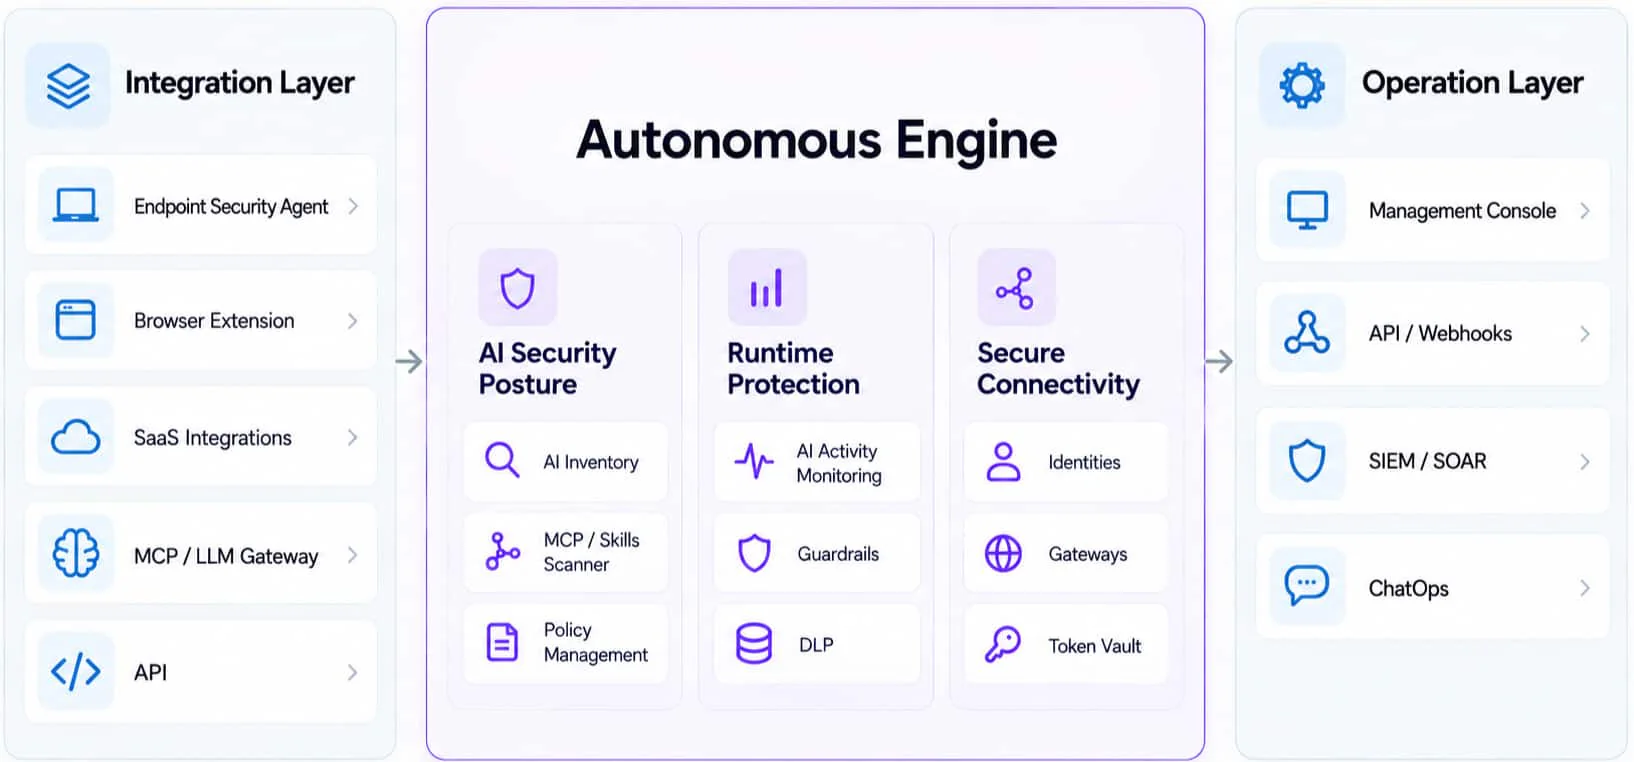
Explore the three core capabilities:
Why Customers Choose Autonomous
Thanks to Autonomous we now have full visibility into Shadow AI and our software supply chain on 4,000 endpoints.
From Control
to Governance

Centralized policy, identity and audit across all agentic activity. The governance plane defines what agents are allowed to do — and enforces it at runtime.
Control various activity operations, tools, MCP servers, authentication methods and many more
Automatically block off-script, unauthorized and dangerous commands
Plugs directly into your security stack, SIEM, and SSO/SCIM with full SOC 2 compliance.
Discover shadow AI and map hidden risks across your endpoints in just 10 minutes

Securing and governing AI agents at the endpoint.
Autonomous Security Inc
135 W. 50th St. Suite 200
New York, NY 10020

Autonomous Security Inc. All rights reserved 2026.